Solution · Access
Single sign-on. One login with MFA for every app.
Every app has its own password, and when someone leaves an account easily stays open. With single sign-on your team signs in once, and you disable one account instead of twenty.
What changes for you
-
Offboarding in one click
Disable one account and file cloud, VPN, business software and admin consoles are closed. No more forgotten access for former staff.
-
MFA everywhere
The second factor applies to every connected app, via app or hardware key. A stolen password alone is no longer enough.
-
Self-service password reset
One password instead of many. Reset by self-service instead of a phone call.
-
Traceable
Who signed in where and when is logged. That helps with audits, ISO 27001 and NIS2.
→
What runs behind it
-
Hosted by you
The sign-in service runs in your infrastructure or a data centre in the EU. No dependency on a cloud account.
-
Highly available
If sign-in fails, everything stops. That is why it runs redundantly and is monitored.
-
Also for older software
Modern apps via OpenID Connect or SAML, older ones via LDAP or a proxy in front.
-
Connected to remote access
The same sign-in opens access to the company network, checking person and device.
→
What it looks like
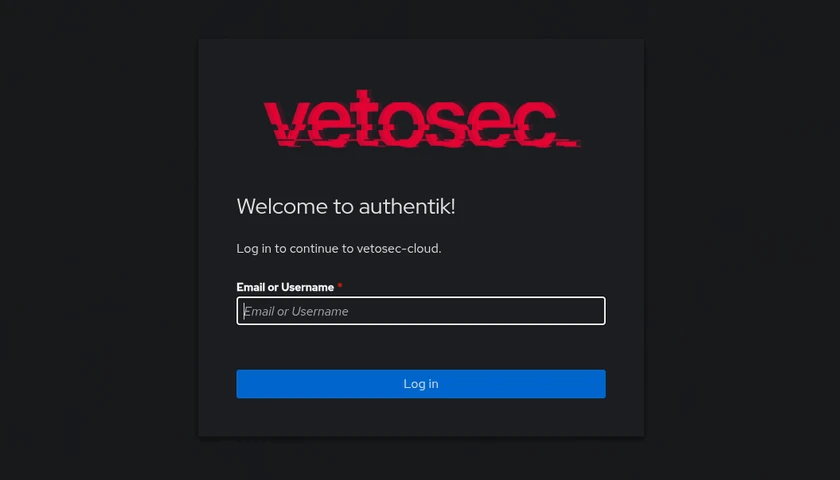
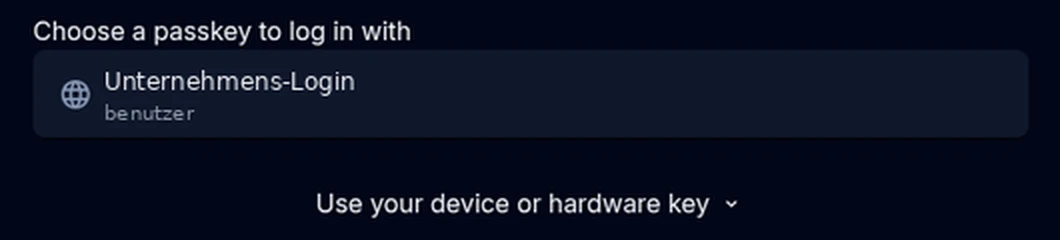
Proof of Concept
Try single sign-on before you switch.
We connect two or three of your apps in a test environment. You see what sign-in feels like for your team.
Service or project
We run it for you, or your team takes over.
As a managed service for a fixed monthly price, with updates, backup and monitoring. Or as a project with handover of network plan, runbook and all credentials.
For IT leads
Technical detailsAuthentik · OIDC · SAML · LDAP
- Identity provider
- Authentik, self-hosted, in containers on hardened Linux.
- Protocols
- OpenID Connect, OAuth 2.0, SAML 2.0 and LDAP. Apps without SSO support via a proxy in front.
- MFA
- TOTP, WebAuthn, passkeys and FIDO2 hardware keys, administrators included.
- Directory
- Own user directory or connection to an existing Active Directory.
- Availability
- Run redundantly and monitored.
- Audit
- Sign-in events logged centrally and analysed in the SIEM.
- Lifecycle
- Self-service password reset. Disabling one account closes every connected app.
Further reading
More on the topic
-
Single sign-on
Single sign-on (SSO) is one central login for many applications: staff sign in once, ideally with a second factor, and reach every app they are allowed to use.
→ -
Two-factor authentication (2FA)
Two-factor authentication asks for a second proof alongside the password at login, such as a code from an app or a security key you plug in.
→ -
Berechtigungskonzept für KMU: Eine einfache Struktur, die funktioniert
A simple, workable access-control model for SMEs.
→
FAQ
Frequently asked questions
What is single sign-on?
Single sign-on means one central login for many apps. The apps trust the sign-in service instead of managing their own passwords.
Do we need this if we have Microsoft 365?
Not necessarily. It pays off with many self-hosted apps or when sign-in should stay in your own infrastructure.
Which technology do you use?
Authentik as identity provider with OpenID Connect, SAML and LDAP, MFA via TOTP or WebAuthn, running in containers on hardened Linux.
Who do you offer this to?
For regulated companies, professions bound by confidentiality and anyone processing sensitive data, and for companies of about 30+ staff with critical systems.
Discuss single sign-on
Free first call
Briefly describe your situation. We help you assess it and plan the next step. Reply within 24 hours on working days.

Single sign-on and identity management with Authentik in Austria
vetosec sets up single sign-on and MFA with Authentik for businesses in Austria.
office [at] vetosec [dot] at · vetosec.at/contact/