How we work
How we build. The same standards for every system.
Every solution follows the same rules for hardening, updates and backup. Here is what we do and what it means for you.
Standards
-
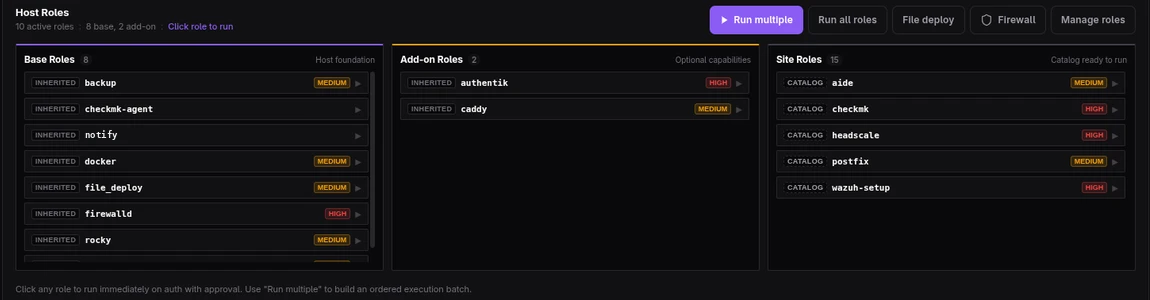
Every server hardened the same way
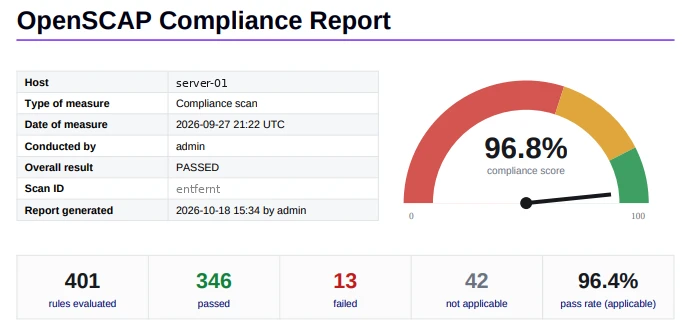
We set up servers automatically to the CIS Benchmark, an internationally recognised security baseline. For you that means no forgotten settings, a provable security level for audits, and a broken server rebuilt in hours instead of days.
→ -
Updates without long downtime
Our services run in containers. An update means starting the new version, checking it, switching over. If something fails we are back in minutes. Moving to new hardware or a data centre needs no reinstall.
→ -
A breach stays contained
Separate networks, personal accounts with MFA and SELinux, which allows each service only what it needs. If one service is compromised, the attacker cannot reach the rest.
→ -
Backups that survive an attack
Local snapshots for fast recovery, an encrypted offsite copy and where needed an immutable copy with S3 Object Lock that even an attacker with admin rights cannot delete. We rehearse restores on a schedule.
→ -
Linux where Windows Server is not needed
Linux handles many Windows Server jobs with lower licence costs and less attack surface, even Windows sign-in via Active Directory. Where business software needs Windows Server, we run it.
→ -
Monitored from day one
Every system reports to our own monitoring platform. An engineer checks every relevant alert; routine runs automatically.
→ -
Documented and yours
You get the network plan, runbook and all credentials. The systems are yours, with no licence tie to us.
Automated
Every server gets the same tested building blocks.
Technology
For the technically curious: the software behind our solutions. Proven, openly audited and free of licence lock-in.
- Proxmox VEVirtualisation & clusters
- ZFSChecksummed storage
- OPNsenseFirewall & segmentation
- WireGuard · NetBirdRemote access
- AuthentikSingle sign-on & MFA
- NextcloudSecured file cloud
- Samba ADUser directory
- Rocky Linux · DebianServer OS
- SELinuxService confinement
- ContainersUpdates & moves
- AnsibleAutomation & hardening
- S3 Object LockImmutable backup
Open source consulting
We use open source where it makes sense. In consulting we check which of your systems can move, what you save and where a commercial product fits better.
-
Lower running costs
Virtualisation, firewall, VPN, backup and single sign-on run without licence or subscription fees. You only pay for optional vendor support.
-
Your data stays with you
Systems run in your server room or in a data centre of your choice in the EU.
-
Independent of vendors
Open standards and formats. Switching vendor or provider stays possible at any time.
-
A clear recommendation
You get a list: what is worth moving, what should stay and what each costs.
FAQ
Frequently asked questions
What is the CIS Benchmark?
A collection of security settings for operating systems and software, published by the Center for Internet Security. It is an international reference for hardened systems and often used in audits.
Do we get your automation?
No. Our automation is our tooling. You get the documentation of your environment: network plan, runbook and all credentials.
Do you support Windows and VMware?
We take over existing systems where they run well. For new builds we recommend what costs least and runs most securely.
Discuss your project
Free first call
Briefly describe your situation. We help you assess it and plan the next step. Reply within 24 hours on working days.

Hardened, highly available open source infrastructure
vetosec builds infrastructure to fixed standards: CIS hardening, SELinux, containers, ZFS, immutable backups, Samba AD, Proxmox, OPNsense, WireGuard, NetBird, Authentik and Nextcloud.
office [at] vetosec [dot] at · vetosec.at/contact/