Warning The vulnerabilities PHP2Shell and HTTP2Shell are being heavily exploited right now. Many websites and servers are affected. Please check here first whether you are affected. Am I affected?
Servers & clusters · Operations
Managed Linux servers. Every change checked.
We keep your Linux servers current and secure. Nothing happens without a test and approval. Everything is recorded.
What you get
-
Updates without surprises
First a dry run, then approval, then the update. The same on every server.
-
Problems spotted early
We watch every server. An engineer looks at every important alert.
→ -
Everything traceable
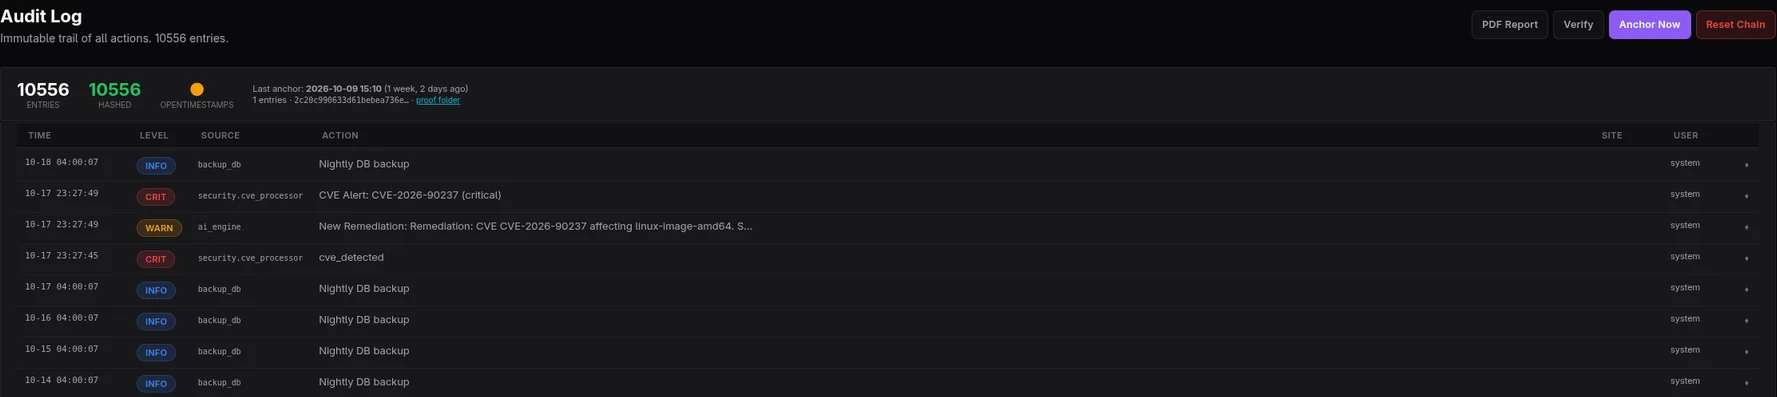
Who changed what, when and why. The log cannot be faked. Good for NIS2 and ISO 27001.
→ -
Security stays high
We check regularly that every server is still as secure as on day one.
→
Example
How an update runs.
-
Hole found. Six servers affected.
-
Dry run. Nothing changed yet.
-
Approval. An engineer approves.
-
Update. The same on all six servers.
-
Logged. Cannot be changed afterwards.
The log
Price
One fixed monthly price. After an assessment.
Fixed monthly price after an assessment. With an in-house IT team we split the tasks in writing.
For IT leads
Technical detailsRHEL · Rocky Linux · AlmaLinux · OpenSCAP · SELinux · Wazuh · firewalld
- Configuration
- Servers, hardening and firewall rules as code, idempotent runbooks, dry run before every change.
- Approval
- Role-based approval with a reason, optional four-eyes principle with your team.
- Audit log
- Every entry carries the SHA-256 hash of the previous one, anchored with a timestamp, export as PDF.
- Monitoring
- Agent per server, file integrity, vulnerabilities and sign-ins in the SIEM, alerts as triggers for runbooks.
- Updates
- Security updates in maintenance windows, staggered across nodes, service checks afterwards.
- Compliance
- Scheduled OpenSCAP scans, report per server with open items.
- AI assistance
- Analysis of output and logs by a language model, execution only by the engineer.
Further reading
-
Monitoring einrichten reicht nicht: Warum Managed Monitoring besser ist
Installing a monitoring tool is quick.
→ -
KI findet Sicherheitslücken am Fließband: Was das für Ihre Server heißt
New AI models find vulnerabilities faster than ever.
→ -
Server absichern: Warum ein Standard-Server nicht mehr reicht
A freshly installed server is set up for convenience.
→
FAQ
Frequently asked questions
Do you work with our IT team?
Yes. Your team can approve changes too. Who does what is agreed in writing.
Do we get access to everything?
To your servers, always. Plus reports, log, network plan and runbook. Our tools stay with us.
Only Red Hat systems?
RHEL, Rocky Linux and AlmaLinux fit best. We look after Debian too.
Who is this for?
For companies with about 30+ staff and anyone whose servers must not stop. With or without an in-house IT team.
Contact
Free first call
Briefly describe your situation. We help you assess it and plan the next step. Reply within 24 hours on working days.

Linux server operations and RHEL support in Austria
vetosec runs RHEL, Rocky Linux and AlmaLinux with patching, monitoring, CIS hardening, approvals and a hash-chained audit log.
office [at] vetosec [dot] at · vetosec.at/contact/