Solution · Resilience
Firewall and segmentation. An infected PC cannot reach your servers.
In many businesses PCs, servers, printers and guest Wi-Fi share one network. We split them into separate zones and maintain the rules so an attack cannot spread.
What changes for you
-
Attacks stay contained
Office, servers, guests, printers and medical or production devices sit in separate networks. Ransomware does not spread freely.
-
A second firewall on standby
Optionally two units that replace each other. If one fails, the internet keeps running.
-
Documented rules
Every rule has a reason and is documented. Old exceptions are removed.
-
No licence subscription
The firewall software needs no subscription. Security updates still arrive regularly.
What runs behind it
-
Default is deny
Between zones only what is explicitly allowed gets through.
-
Remote access built in
Remote staff and sites connect encrypted, with per-person rights.
→ -
Logs in monitoring
Suspicious connections land on our platform and are checked.
→ -
Yearly review
Once a year we go through the rules with you.
What it looks like
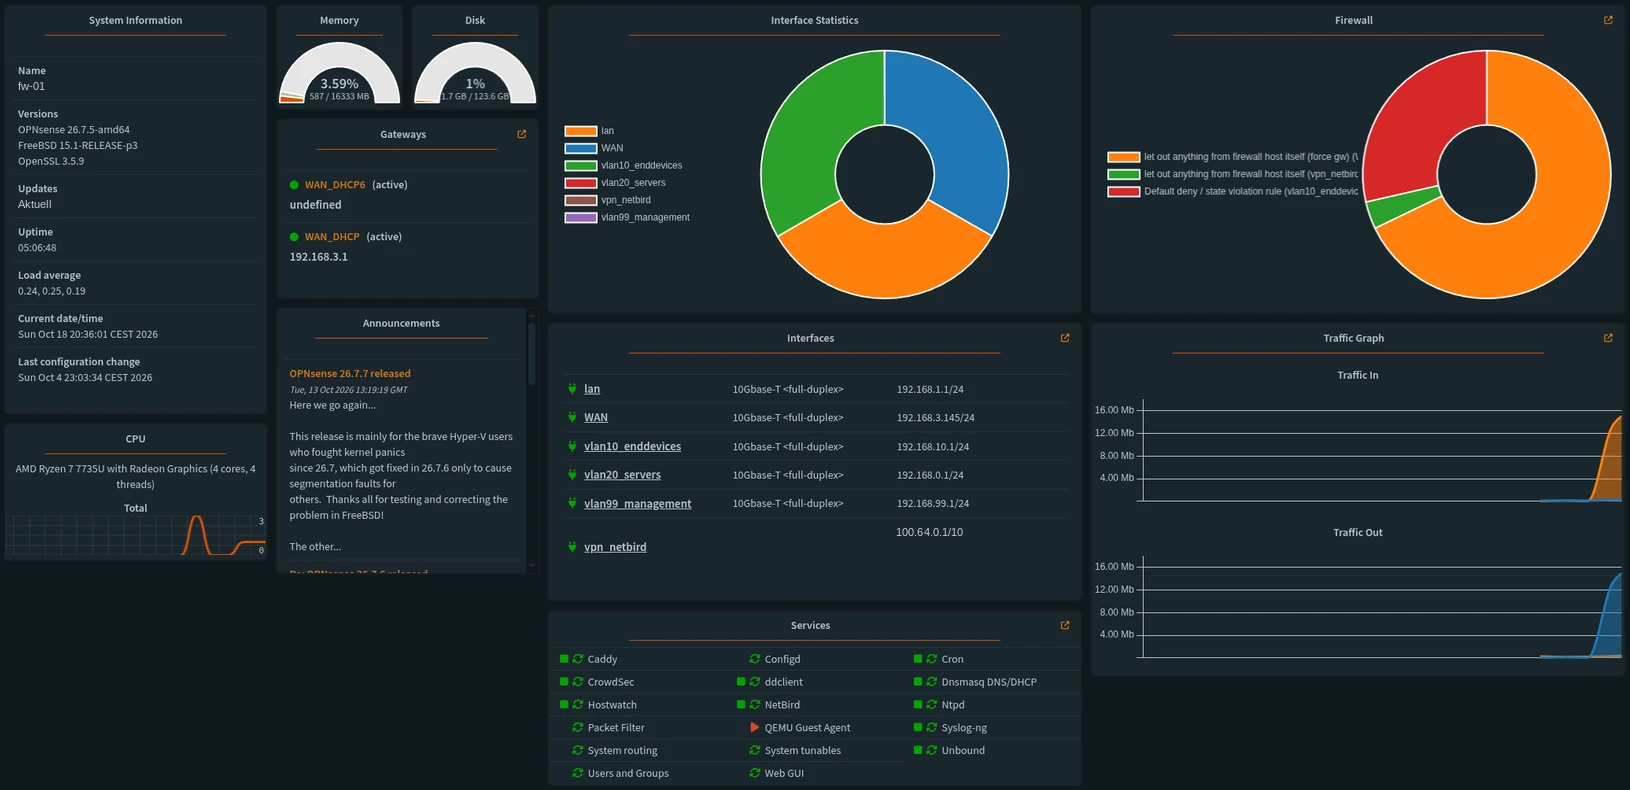
What we set up
Thought through in detail.
-
Clean zones and a dedicated management zone
Office, servers, guests and devices in separate networks. Admin interfaces of servers, switches and the firewall are only reachable from a dedicated management zone.
-
Multiple internet uplinks
Two or more uplinks with load balancing and automatic failover. If one provider fails, the business keeps running over the other.
-
Known attackers stay out
Shared blocklists block addresses that have already attacked elsewhere, before they try with you.
-
Own DNS with split DNS
Internal names resolve in the office and via remote access, while the structure stays invisible from outside. Optionally, blocklists stop known malicious sites at name resolution.
-
Remote access built in
WireGuard for sites and NetBird for per-person access run directly on the firewall, with the same zones and rules.
→ -
Two firewalls, one rule set
Highly available if you want: both units sync rules and connections, a failure interrupts nothing.
-
Logs in monitoring
Firewall logs land on our platform. An engineer sees suspicious patterns before they turn into an incident.
→ -
Configuration backed up and documented
Every change is backed up and traceable. A replacement unit is back on the same state quickly.
Service or project
We run it for you, or your team takes over.
As a managed service for a fixed monthly price, with updates, backup and monitoring. Or as a project with handover of network plan, runbook and all credentials.
For IT leads
Technical detailsOPNsense · CARP · WireGuard · CrowdSec
- Platform
- OPNsense, open source, with regular security updates.
- Zones
- VLANs for office, servers, guests and devices, plus a dedicated management zone. Default deny.
- Uplinks
- Multiple uplinks with load balancing and automatic failover.
- High availability
- Optionally two units with CARP and synchronised rules and connection state.
- Remote access
- WireGuard for sites, NetBird for per-person access, using the same zones.
- Blocklists and detection
- Community blocklists (CrowdSec), optional intrusion detection.
- DNS
- Own resolver with split DNS, optional DNS blocklists.
- Logging
- Firewall logs in the SIEM, configuration backed up and versioned.
Further reading
More on the topic
-
Firewall
A firewall is a control point between your company network and the internet that permits or blocks every connection according to fixed rules.
→ -
Network segmentation
Network segmentation divides a company network into separate zones, with only expressly permitted connections between them.
→ -
Netzwerksegmentierung für KMU: Klein anfangen, Wirkung erzielen
A practical approach to network segmentation for SMEs.
→
FAQ
Frequently asked questions
Is the provider's router firewall enough?
It protects against open access from the internet but does not separate internal networks. That is exactly where attacks spread.
Which technology do you use?
OPNsense, an open source firewall with regular security updates, VLANs, CARP high availability, WireGuard and optional intrusion detection.
Do we have to change the cabling?
Usually not. Separation uses VLANs on existing switches, as long as they support it.
Who do you offer this to?
For regulated companies, professions bound by confidentiality and anyone processing sensitive data, and for companies of about 30+ staff with critical systems.
Discuss your firewall
Free first call
Briefly describe your situation. We help you assess it and plan the next step. Reply within 24 hours on working days.

OPNsense firewall and network segmentation in Austria
vetosec sets up OPNsense firewalls with segmentation, HA and VPN for businesses in Austria.
office [at] vetosec [dot] at · vetosec.at/contact/