Solution · Access
Remote access and VPN. Secure access to the company network from home and other sites.
A classic VPN often opens the whole company network, outside vendors included. We set up access per person and device, with a second factor at sign-in.
What changes for you
-
Access only to approved systems
Accounting sees accounting, the maintenance contractor only their machine. A stolen laptop does not open the whole network.
-
Vendors with an expiry date
Outsiders get access for one appointment and one system. Afterwards it closes automatically.
-
Sites like one network
Branches, warehouse and data centre are connected and still separated from each other.
-
Simple for staff
Sign in once and the connection is up. No profiles or certificates to install.
What runs behind it
-
Modern encryption
A lean, audited VPN protocol with fixed modern ciphers. Less code means less attack surface.
-
No exposed admin ports
Servers and admin consoles are unreachable from the internet, only via remote access.
-
Sign-in with MFA
Via your single sign-on. Account disabled means access disabled.
→ -
Self-hosted
The control plane runs in your infrastructure; your connection data sits with no third party.
What we set up
Thought through in detail so your team never notices it.
-
Access by role
Policies per group: staff, servers, vendors. Every connection is explicitly allowed, everything else stays closed.
-
Device checks before access
Only devices with a current operating system and client get in. Outdated or unknown devices stay out.
-
Internal names at home
Servers are reachable by their internal names, even from home. All other internet traffic goes direct and stays fast (split DNS).
-
Existing networks included
Printers, phone systems or machines in the office network are reachable without a client on every device. Redundant over two paths if you want.
-
Direct connections
Devices connect directly and encrypted. A detour via a relay server is only used when there is no other way.
-
Log of every connection
Who was connected to which system and when. That helps in audits and in an incident.
What it looks like
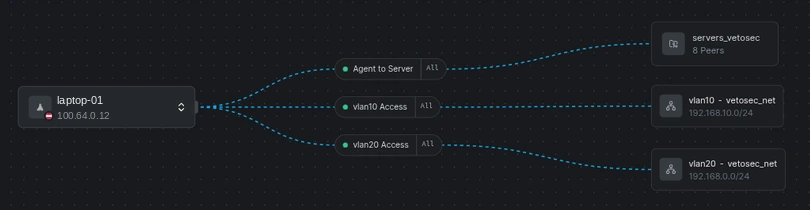
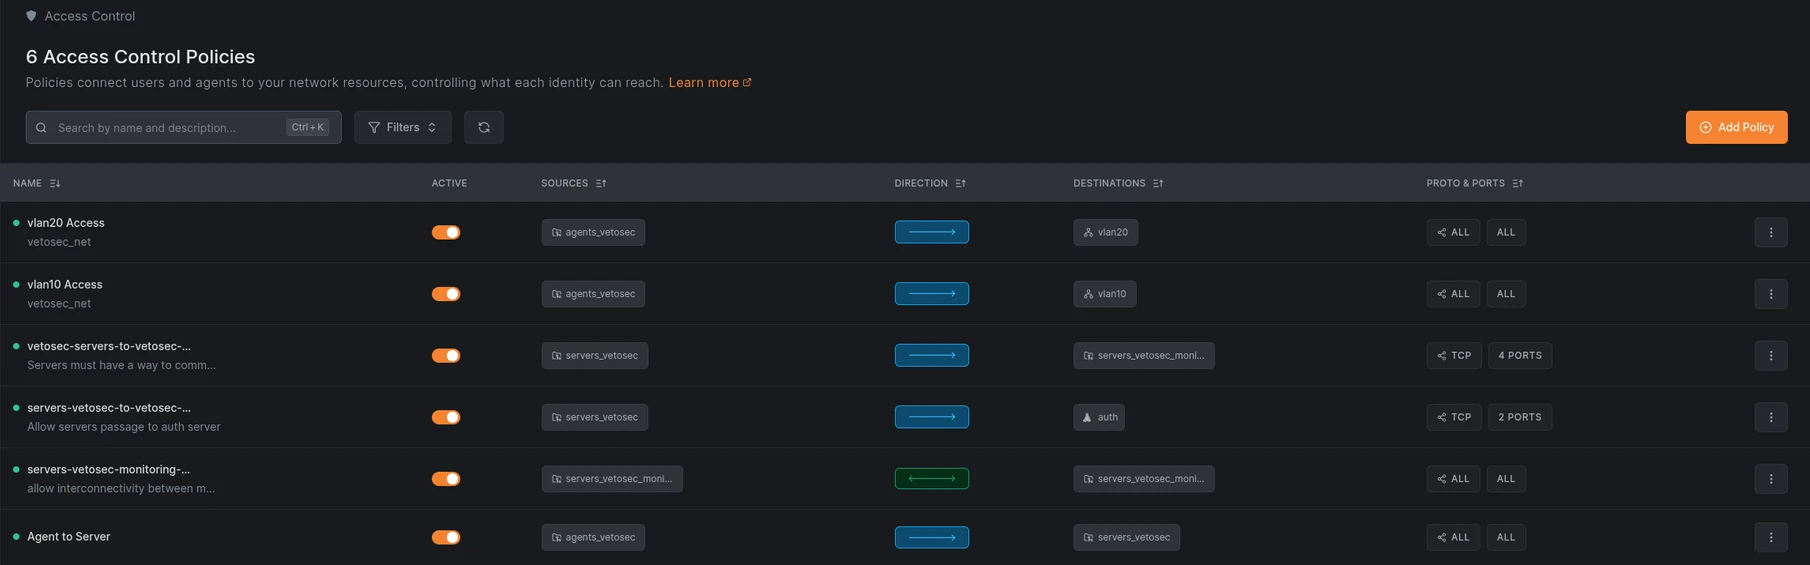
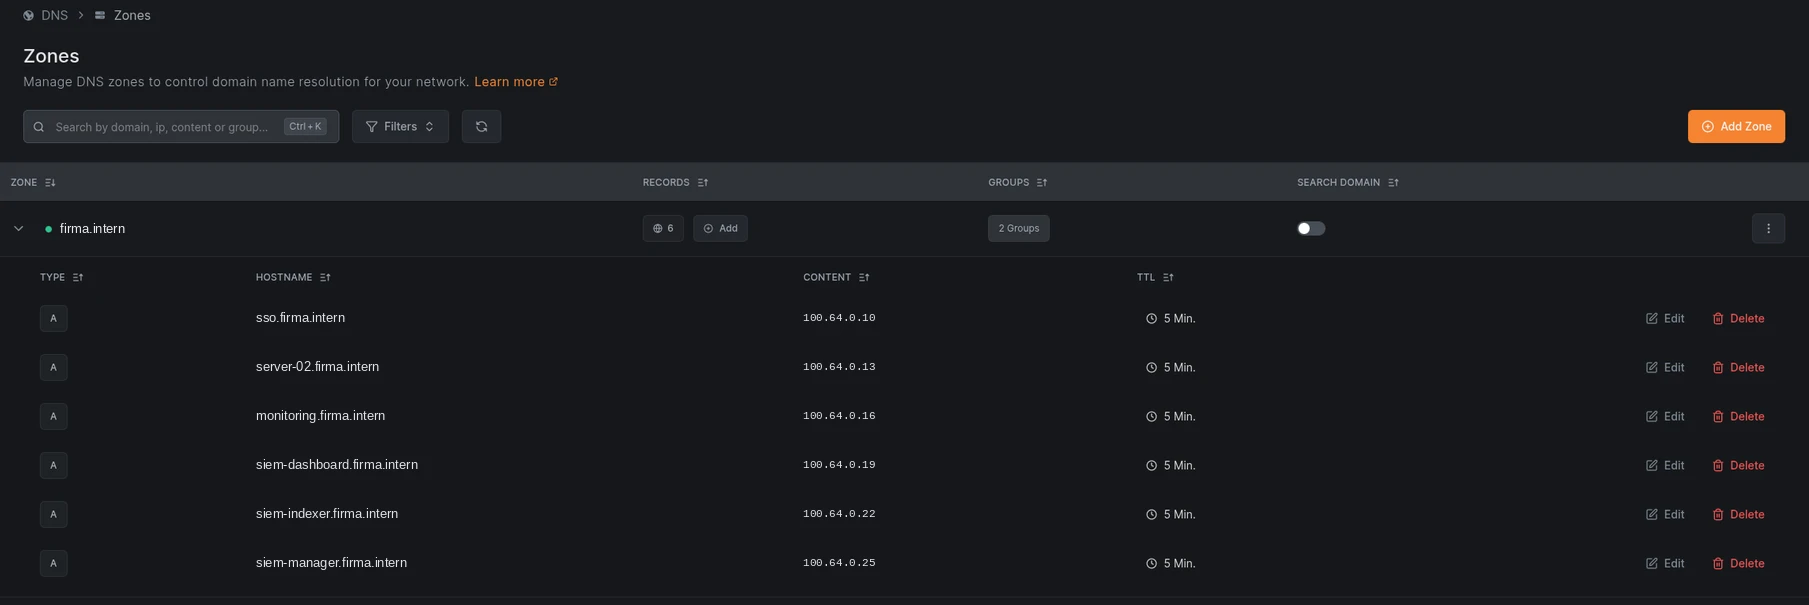
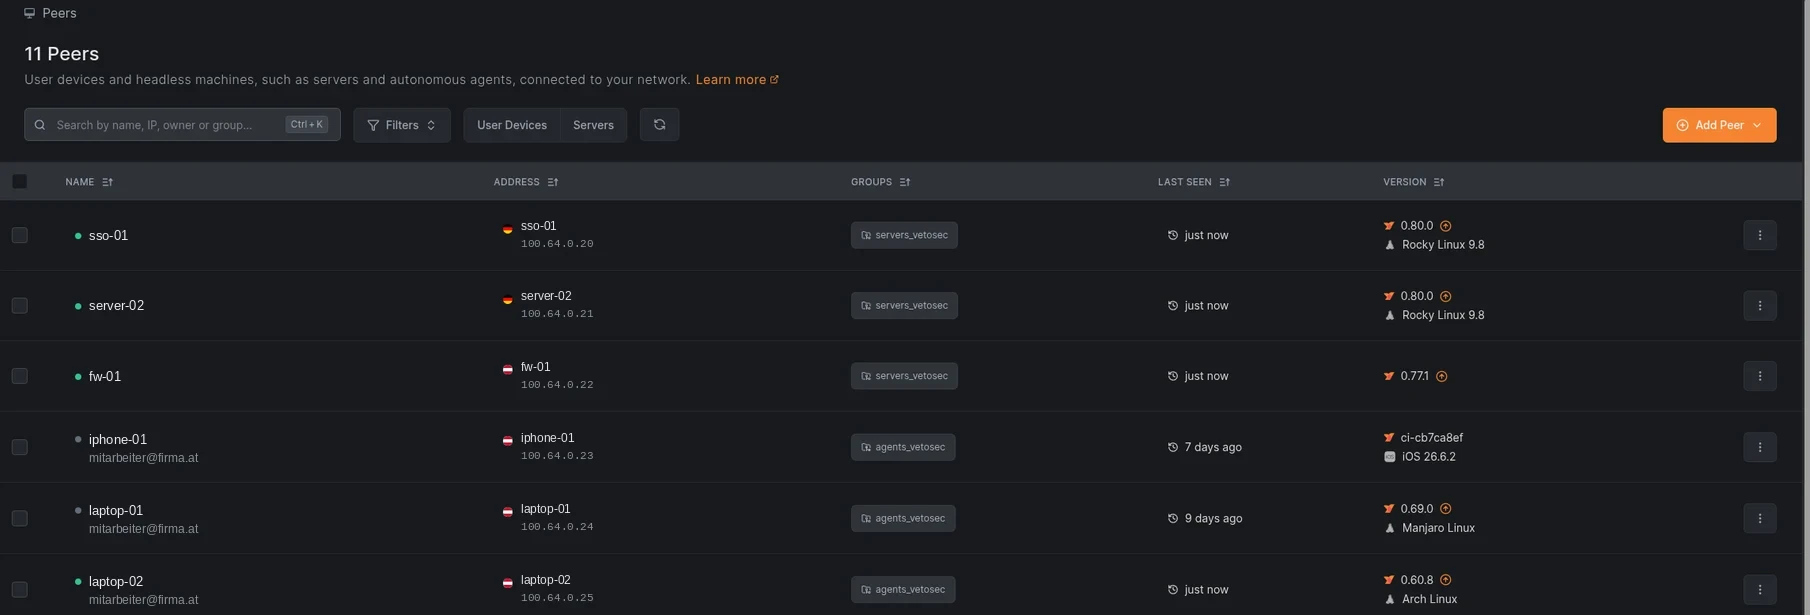
Proof of Concept
Try remote access before you switch.
We connect a few devices to a test system. You see how sign-in works and how precisely access can be controlled.
Service or project
We run it for you, or your team takes over.
As a managed service for a fixed monthly price, with updates, backup and monitoring. Or as a project with handover of network plan, runbook and all credentials.
For IT leads
Technical detailsNetBird · WireGuard · Authentik
- Zero trust network access
- NetBird, self-hosted. The control plane runs in your infrastructure.
- Data plane
- WireGuard, direct encrypted connections between devices, relay only as fallback.
- Authentication
- Authentik via OpenID Connect with MFA.
- Policies
- Per group with source, destination, direction and port. Default deny.
- Posture checks
- Minimum OS and client versions before access.
- Networks without a client
- Routing into existing subnets for printers, telephony and machines, optionally redundant.
- DNS
- Internal zone with split DNS, all other traffic goes straight to the internet.
- Sites
- Fixed site-to-site links with WireGuard.
- Audit
- Connection events per person and system.
Further reading
More on the topic
-
VPN
A VPN (virtual private network) is an encrypted connection that lets staff working away from the office dial into the company network.
→ -
Zero trust
Zero trust is a security model in which every request for access is verified on its own, including requests that come from inside the company network.
→ -
Netzwerksegmentierung für KMU: Klein anfangen, Wirkung erzielen
A practical approach to network segmentation for SMEs.
→
FAQ
Frequently asked questions
How is this different from a classic VPN?
A classic VPN puts the device inside the company network. With per-person and per-device access each connection reaches only approved systems. That is called zero trust.
Which technology do you use?
NetBird for per-person and per-device access with sign-in via Authentik, WireGuard for fixed links between sites. Both self-hosted.
Does this work with our existing firewall?
In most cases yes. We check upfront and adjust the rules.
Who do you offer this to?
For regulated companies, professions bound by confidentiality and anyone processing sensitive data, and for companies of about 30+ staff with critical systems.
Discuss remote access
Free first call
Briefly describe your situation. We help you assess it and plan the next step. Reply within 24 hours on working days.

VPN and zero trust network access for businesses in Austria
vetosec sets up secure remote access in Austria with NetBird, WireGuard, SSO and MFA.
office [at] vetosec [dot] at · vetosec.at/contact/