Monitoring and logging
Monitoring as plug & play. We monitor, you get the report.
We install an agent on your systems and do the rest. An engineer checks every important alert, you get a monthly report and hear from us right away when something is wrong. If you want, we also take over updates.
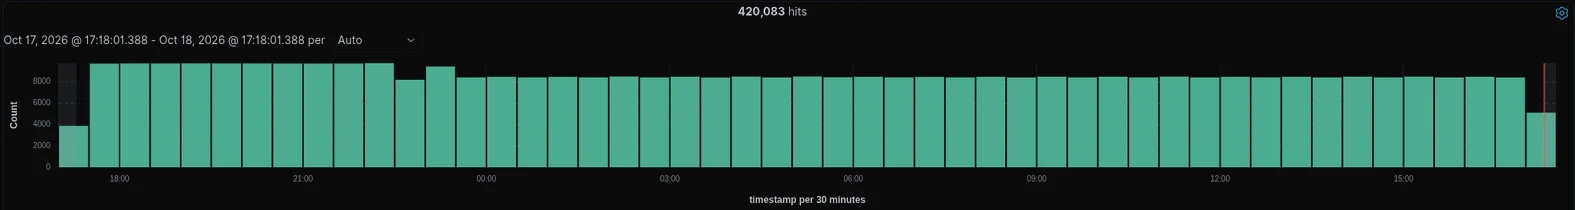
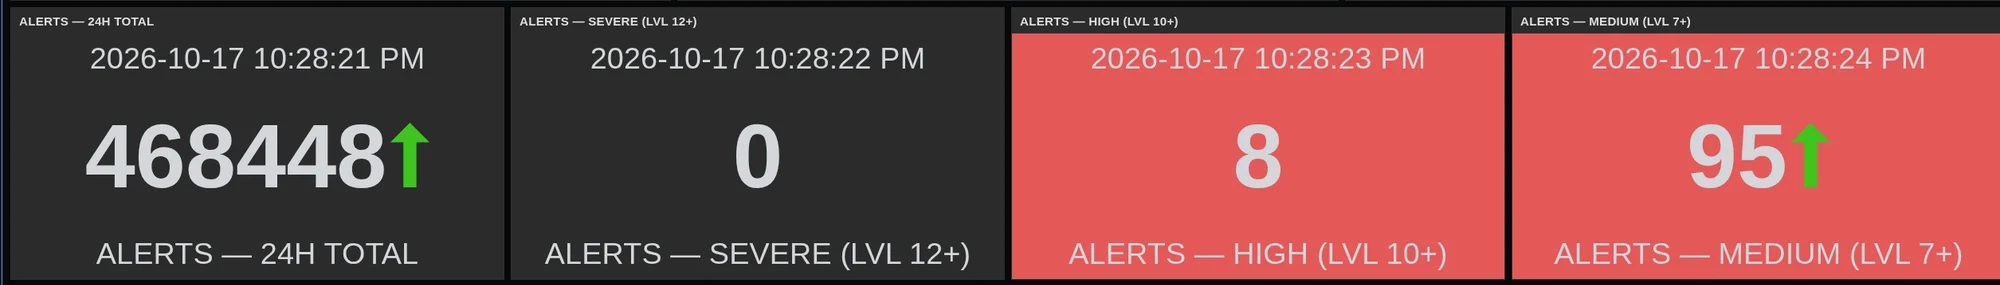
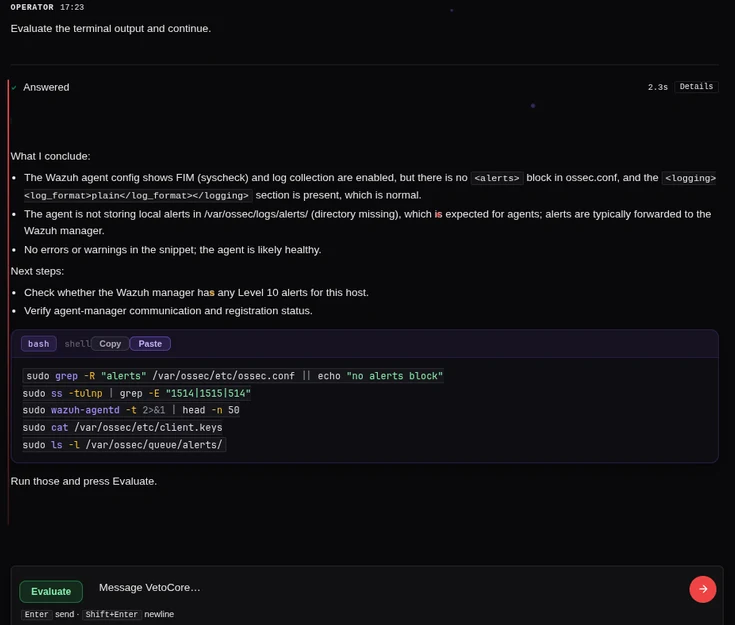
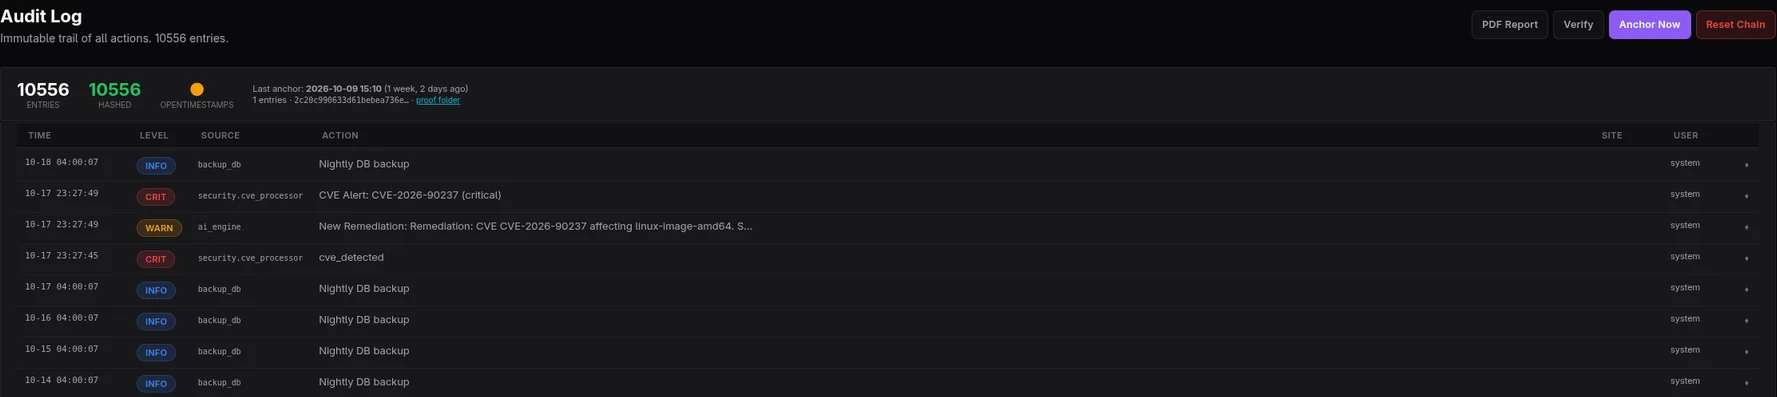
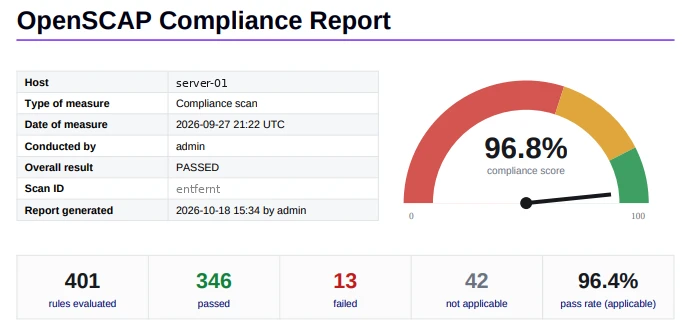
Inside our platform
From live operations, host names and addresses removed.
For IT leads
Technical detailsAgent · SIEM · compliance scans · audit log
- Collection
- Agent on the servers, plus logs from firewalls, network, virtualisation and storage.
- Coverage
- Availability, resources, backup runs, sign-ins and security events in one view.
- Triage
- Rules filter false alarms, an engineer checks every relevant alert.
- Compliance
- Servers are checked automatically against recognised security baselines, open items are in the report.
- Audit trail
- Actions go into a chained, timestamped log that cannot be altered afterwards.
- Reporting
- Monthly report with incidents, fixes, open updates and the state of the environment.
- Service levels
- Response times by agreement, around the clock via fixed cooperation partners.
FAQ
Frequently asked questions
How quickly is monitoring set up?
Usually within a few days. We install an agent on your systems, set up the rules and send the first report after one month.
What is in the monthly report?
What happened, what we fixed, open updates and where your environment stands. Short and readable.
Are there guaranteed response times?
Yes, by agreement. For around-the-clock service levels we work with fixed cooperation partners.
What is the difference between monitoring and logging?
Monitoring watches the state and alerts when a value leaves its range. Logging records events. Operations need monitoring; investigating an incident needs the logs.
Do I need this for NIS2?
NISG 2026 requires incident handling, among other things. Without logs an incident can neither be reported nor reconstructed. This is our view, not legal advice.
Discuss monitoring
Free first call
Briefly describe your situation. We help you assess it and plan the next step. Reply within 24 hours on working days.

Monitoring, logging and SIEM for companies in Austria
vetosec runs infrastructure and security monitoring (SIEM) on its own platform, with an engineer checking every relevant alert.
office [at] vetosec [dot] at · vetosec.at/contact/